
Yoba Crypto Miner Campaign Uses Signed AI Binaries to Deploy Malicious DLLs
Threat actors use signed OpenAI and Anthropic executables to sideload malicious DLLs and run crypto miners under the guise of AI desktop apps.
13 stories
Threat actors use signed OpenAI and Anthropic executables to sideload malicious DLLs and run crypto miners under the guise of AI desktop apps.
FortiBleed 2.0 uncovered 40,573 exposed credentials, while PHP2Shell scanning continues across 5 million WordPress sites.
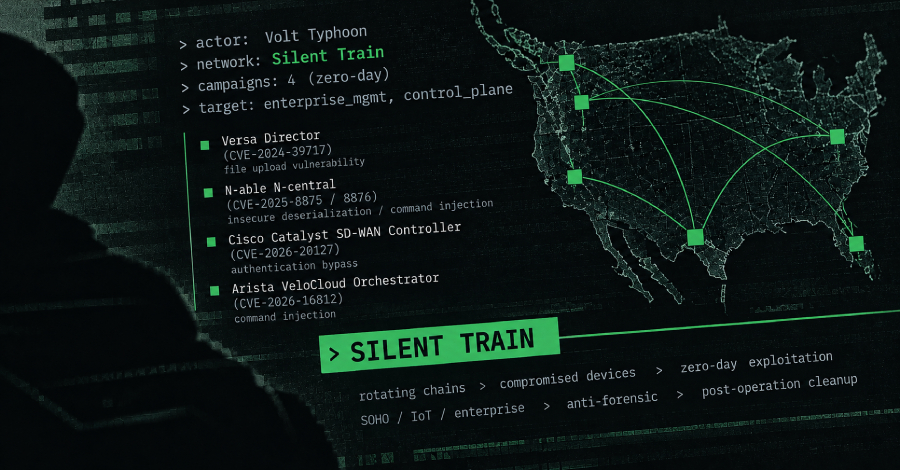
China-linked Volt Typhoon leveraged the Silent Train covert network to deliver four zero-day exploits CVE-2024-39717, CVE-2025-8875.

OVHcloud’s GitHub account was accessed by actors linked to the GlassWorm threat group, resulting in credential theft and malicious code injection into private.
MATCHBOIL, a C# downloader used by UAC-0099, has evolved with enhanced obfuscation and sandbox detection. In December 2025, a manufacturing firm was infected.
Examine recent threat intelligence findings detailing GlassWorm VS Code theme extensions, ransomware affiliate betrayals, and open access infrastructure.

Law enforcement arrested a Venezuelan cartel malware developer linked to international ATM jackpotting operations, targeting physical banking infrastructure.
The FBI and international partners revealed that China-linked Integrity Technology Group ran a portal granting third parties access to stolen emails.
Microsoft's 13-million-follower Twitter account was hijacked to promote a fraudulent cryptocurrency campaign featuring Clippy.

Russian cyber-espionage group UAC-0099 has upgraded its flagship MatchBoil malware dropper with stealthier techniques in recent campaigns targeting Ukrainian.
JPCERT/CC reports a sharp rise in personal data leaks across Japanese organizations driven by mobile API abuse and Metabase vulnerabilities.
Security analysts discover threat actors abusing legitimate Action1 RMM tool installations delivered through deceptive phishing emails and VBS scripts.

The Cisco 0-Day vulnerability, tracked as CVE-2026-76460, is a maximum-severity security flaw that allows an unauthenticated.